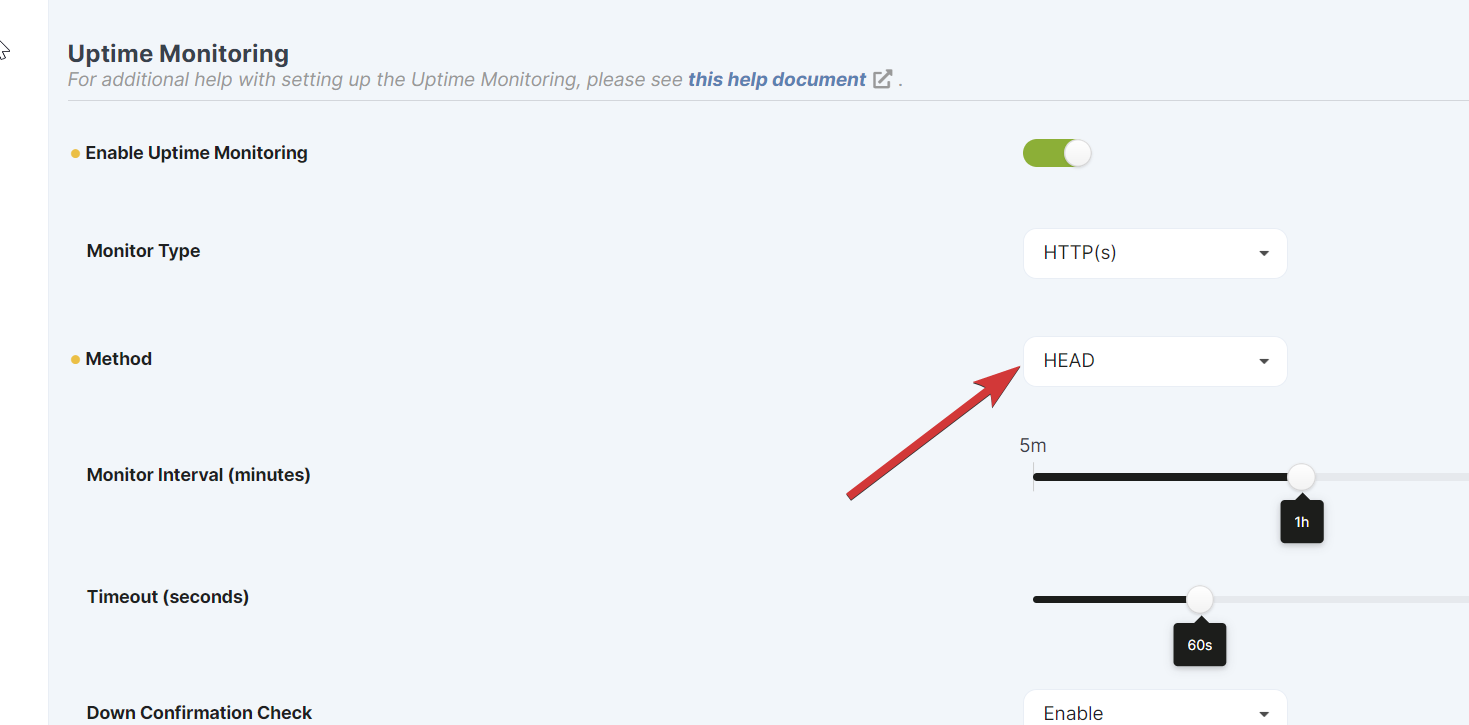
The connection monitor in MainWP is reporting that sites are down because requests are triggering OWASP rule 920170.
This is because a GET request from MainWP has a non-zero Content-Length header, which is invalid.
While it is possible to disable this rule, this leaves servers open to a range of attacks that the rule is designed to block. I haven’t logged the additional data (yet) but if it’s meaningful, perhaps a POST request would be more appropriate.
Great! Thank you for testing it and letting us know.
WordPress® is a registered trademark of the WordPress Foundation, and WooCommerce® is a registered trademark of WooCommerce, Inc. MainWP is an independent product and is not affiliated, associated, or endorsed by the WordPress Foundation, WooCommerce, Inc., or Automattic Inc., except where noted under the Jetpack® API and Trademark License Agreement. All product names, logos, and brands are property of their respective owners and are used for identification purposes only.